Security and privacy findings you can prove.
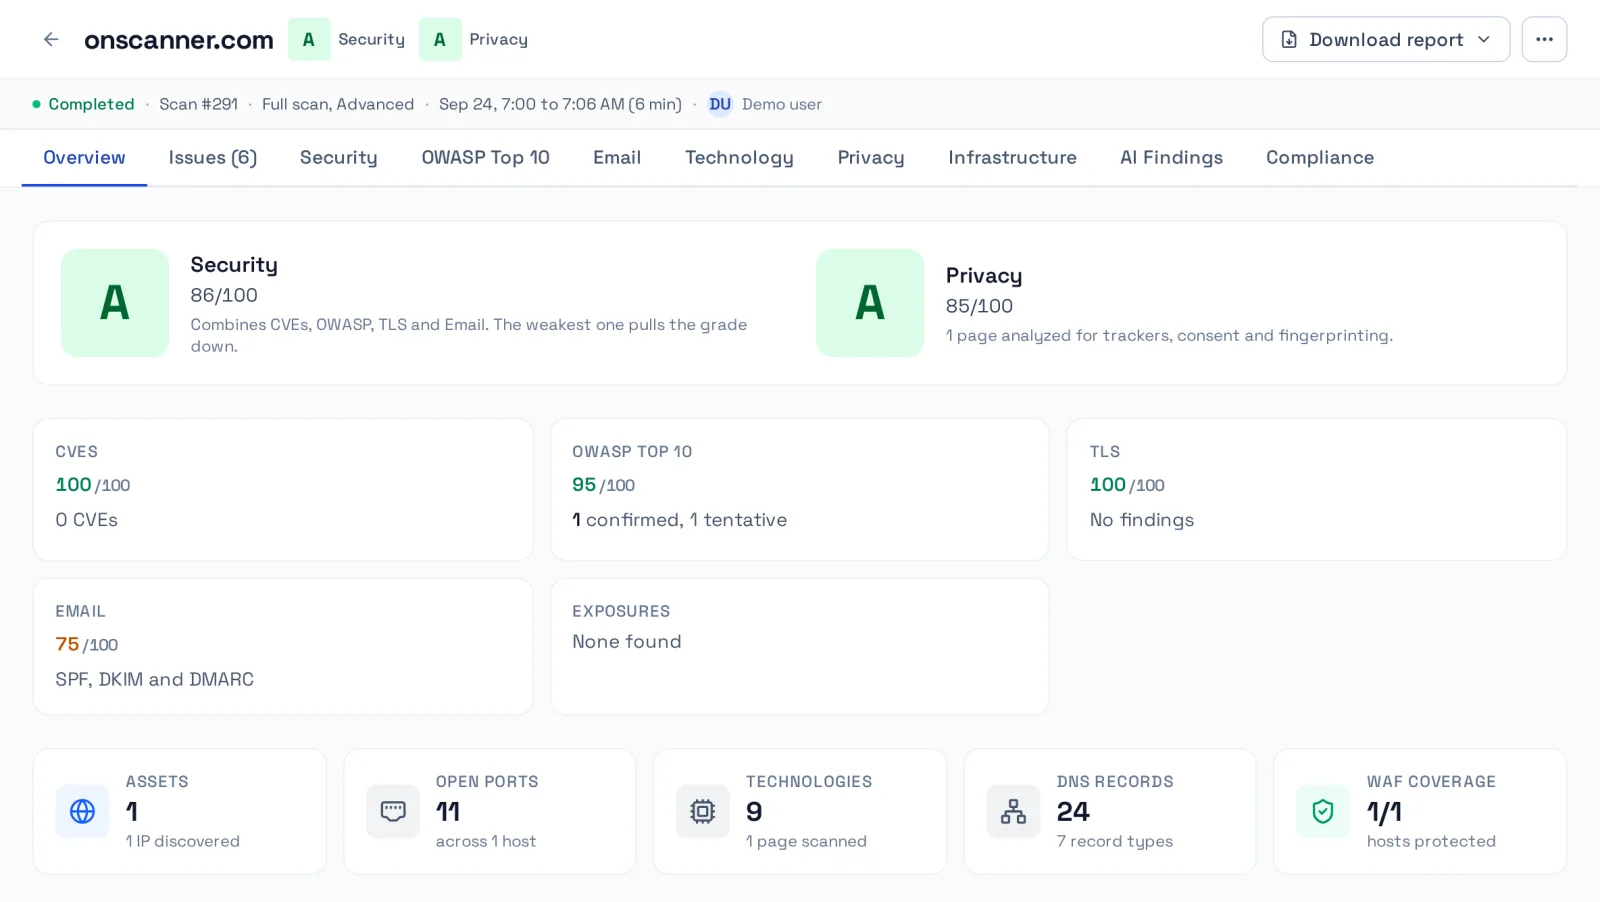
OnScanner is Byte Optimizer's live, on-demand scanner for websites, web apps and APIs. One scan checks vulnerabilities, OWASP Top 10, TLS, email security, trackers, consent and Global Privacy Control, and every finding comes with the evidence behind it.
Free plan, no card required. Plans and pricing live on onscanner.com.
See OnScanner in 76 seconds.
Security, privacy, compliance, AI Findings and monitoring in one 1:16 tour, from one scan to the report you share.
Read the transcript
Every website tells two stories. The one you publish, and the one an attacker, or a regulator, can see. OnScanner shows you both, with findings you can prove. Point it at your domain. Specialist engines run in parallel, signed out, or behind your login. Security. OWASP Top 10, API checks, and CVEs on your real stack, with safe exploit checks that confirm what is actually exploitable. Privacy. A real browser records every tracker, pixel, and cookie. Then it tests whether your consent banner and Global Privacy Control are really honored. Compliance. Scan evidence, mapped to controls across seven frameworks, from SOC 2 and ISO 27001, to GDPR. AI Findings. A plain-language summary, attack chains, and a MITRE ATT&CK kill chain. Then keep watch. Monitoring re-scans on a schedule, and alerts you when something changes. Connect your AI agent over MCP, gate every release, and share a clean PDF report. Evidence. Not guesses. OnScanner. Security and privacy findings you can prove. onscanner.com.
What one scan checks.
Security, privacy, or both in a full scan. Quick, advanced or deep modes, unauthenticated or behind a login.
Web application and API security
OWASP Top 10 dynamic testing and API checks against the live target.
Known vulnerabilities
Detected software matched to CVEs with EPSS and CISA KEV context, plus optional safe, in-band exploit checks.
TLS, email and infrastructure
TLS versions, ciphers and certificates; SPF, DKIM and DMARC; WAF detection and technology fingerprinting.
Exposures and end-of-life
Open ports, exposed files and paths, optional subdomain discovery, and software past end-of-life.
Privacy and trackers
A real browser records trackers, pixels, cookies, fingerprinting and session recorders, with third parties your policy does not name.
Consent and Global Privacy Control
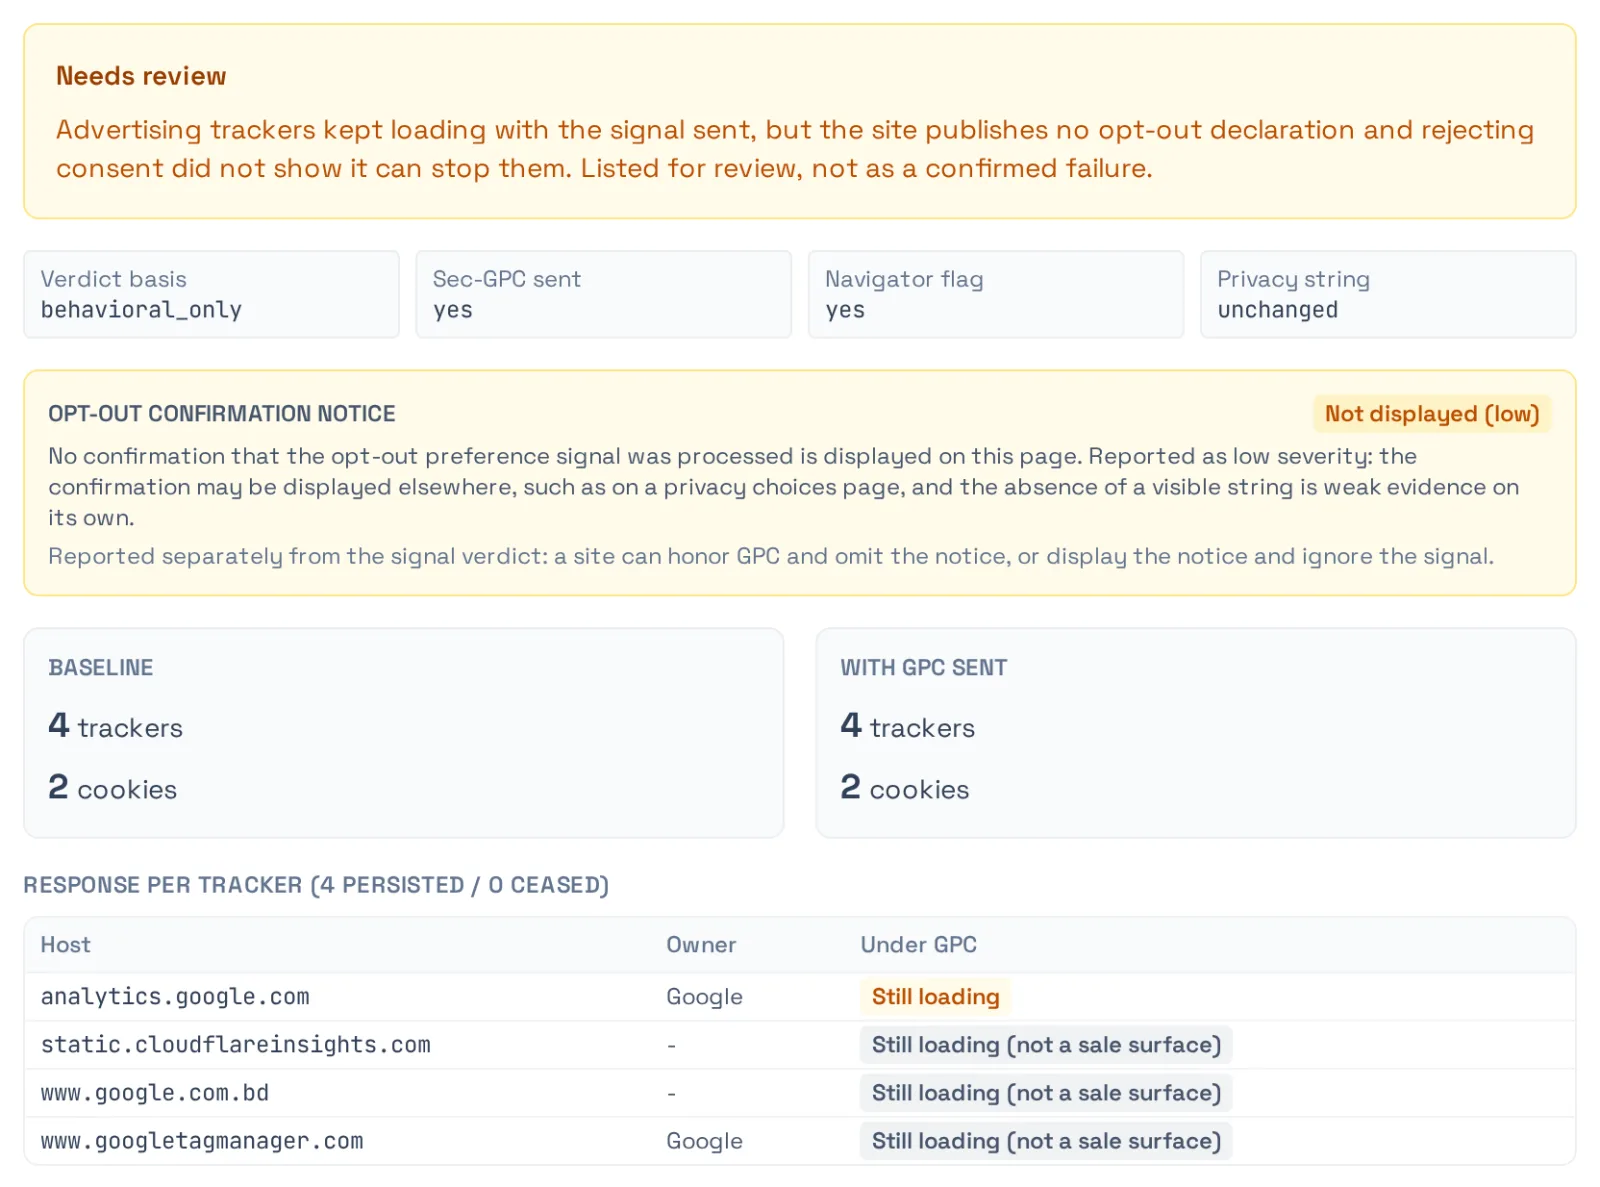
Clicks "Reject all" and "Accept all", compares what loads, and checks whether your site honors GPC signals.
Compliance evidence
Findings mapped to controls in frameworks such as SOC 2, ISO 27001, GDPR, HIPAA and PCI DSS. Evidence for your compliance work, not a certification.
Monitoring and reports
Live, never-cached results, scheduled scans and PDF reports you can share.
REST API and MCP server
Run scans from CI, pull structured results, or let AI agents such as Claude and Cursor scan through MCP.
Your banner says no. Does your site listen?
OnScanner loads your site in a real browser, sends a Global Privacy Control signal, clicks "Reject all", and records which trackers and cookies keep loading anyway. Every verdict shows the requests behind it, so you can fix the tag instead of arguing about it.
- Consent banner checks for both "Reject all" and "Accept all"
- Global Privacy Control behavior, tracker by tracker
- Third parties your privacy policy does not name
Where OnScanner fits in Byte Optimizer.
OnScanner is one of the products Byte Optimizer builds and operates. It gives teams breadth: repeatable, automated coverage of the security and privacy basics, run as often as they ship.
Some problems need depth that no scanner has: chained exploits, business-logic flaws, and judgment about what a finding means for a specific business. That is what our penetration testing and compliance and privacy services are for. Use OnScanner on its own, or alongside them.
OnScanner questions.
What does OnScanner check?
OnScanner checks websites, web apps and APIs for OWASP Top 10 vulnerabilities, known CVEs with EPSS and CISA KEV context, TLS and email security (SPF, DKIM, DMARC), exposed services and files, and end-of-life software. Its privacy scan records trackers, cookies, fingerprinting and session recorders in a real browser, and tests whether your consent banner and Global Privacy Control signals are respected.
Does OnScanner send my data to an AI model?
The scan engines never call an LLM. AI Findings is optional and opt-in: only when an account owner or admin turns it on are completed results analyzed for executive summaries, ranked risks and MITRE ATT&CK mapping.
Is there a free plan?
Yes. OnScanner has a Free plan that needs no card. Current plans and pricing are on onscanner.com.
How is OnScanner different from a penetration test?
OnScanner is automated and repeatable, ideal for catching known issues and regressions between engagements. A penetration test is a manual assessment that chains weaknesses to prove real impact, including business-logic flaws no scanner can find. Byte Optimizer offers both.
Run your first scan.
OnScanner lives at onscanner.com, with a free plan to start. Questions about fit, volume or a pilot? Talk to us.